Authentication
Xara uses API tokens to authorize requests that manage resources belonging to a business. You can obtain your token from the Xara developer dashboard.
Send the token
Include the token in the Authorization header using the Bearer scheme:
Authorization: Bearer YOUR_API_TOKEN
The adjacent example shows the complete header in a request to retrieve products.
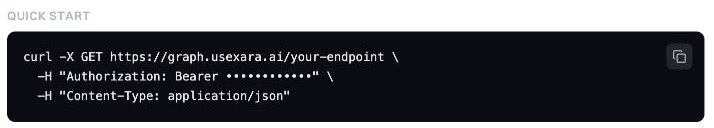
The dashboard uses a masked placeholder in its starter request. Use your real token only in secure server-side code.
Which endpoints require it?
| Operation | Authentication |
|---|---|
| Create a product | Bearer API token |
| Retrieve products | Bearer API token |
| Create a ticket | Bearer API token |
| Request an invoice | No token; uses business_id |
| Receive a webhook | No Bearer token; verify X-Xara-Signature |
Keep tokens on your server
API tokens authorize access to business resources. Never place them in browser code, mobile application bundles, public repositories, screenshots, or support messages.
Store the token in an environment variable:
XARA_API_TOKEN=your_token_here
Then read it only from your backend application.
Authentication errors
A missing or invalid token causes an authentication error. Correct the token before sending the request again.
Check that:
- The header begins with
Bearer. - The token has no extra quotes or whitespace.
- You copied the token from the Xara developer dashboard.